
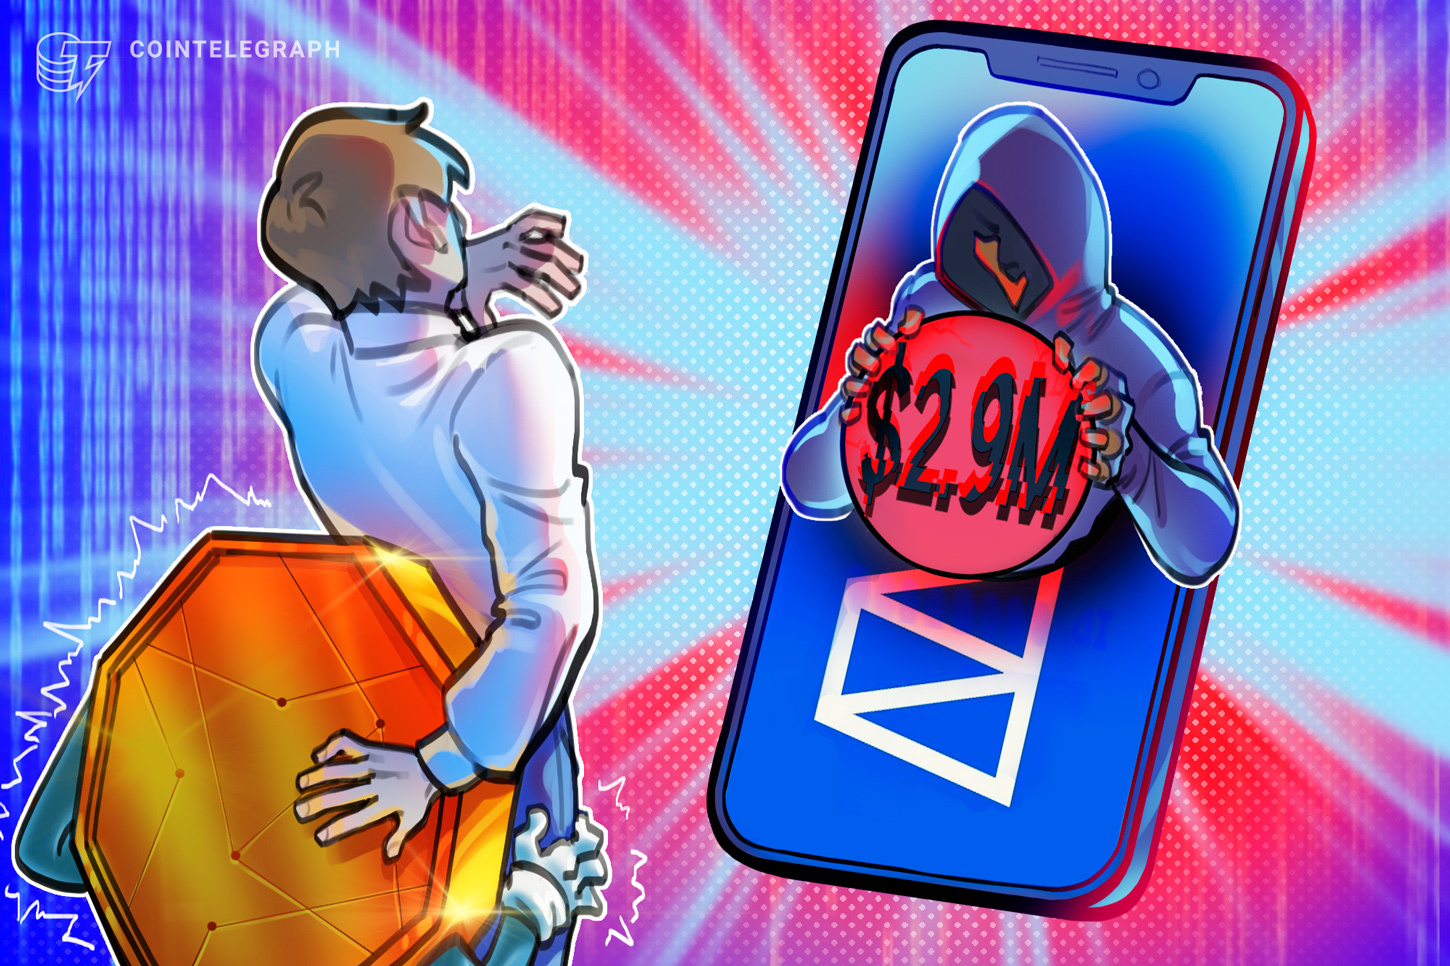
Polymarket said it contained the compromise and removed the affected dependency after attackers injected a malicious script into its frontend.
A third-party vendor compromise discovered Thursday allowed attackers to inject a malicious script into Polymarket's frontend, affecting multiple users.
Blockchain analyst Specter said the malicious script appeared to facilitate a phishing attack that drained an estimated $2.94 million from at least 11 Polymarket user wallets.
Polymarket said on X that the compromise has been contained and that the affected dependency has been removed. It added that users would be fully refunded.

You can get bonuses upto $100 FREE BONUS when you:
💰 Install these recommended apps:
💲 SocialGood - 100% Crypto Back on Everyday Shopping
💲 xPortal - The DeFi For The Next Billion
💲 CryptoTab Browser - Lightweight, fast, and ready to mine!
💰 Register on these recommended exchanges:
🟡 Binance🟡 Bitfinex🟡 Bitmart🟡 Bittrex🟡 Bitget
🟡 CoinEx🟡 Crypto.com🟡 Gate.io🟡 Huobi🟡 Kucoin.








Comments